INSIGHTS
Charities and public sector need compliant tech too
Small charities and community groups hold some of the most sensitive data in any town, often on the least protected IT. That is not a criticism. It is just what we keep finding.
This week we onboarded another small community organisation. Lovely people, doing brilliant work on a shoestring. What made this one different was how it started. A new manager had just joined, and she knew straight away that compliance was a big problem. She came to us because we had sorted the same thing out for her at a different charity.
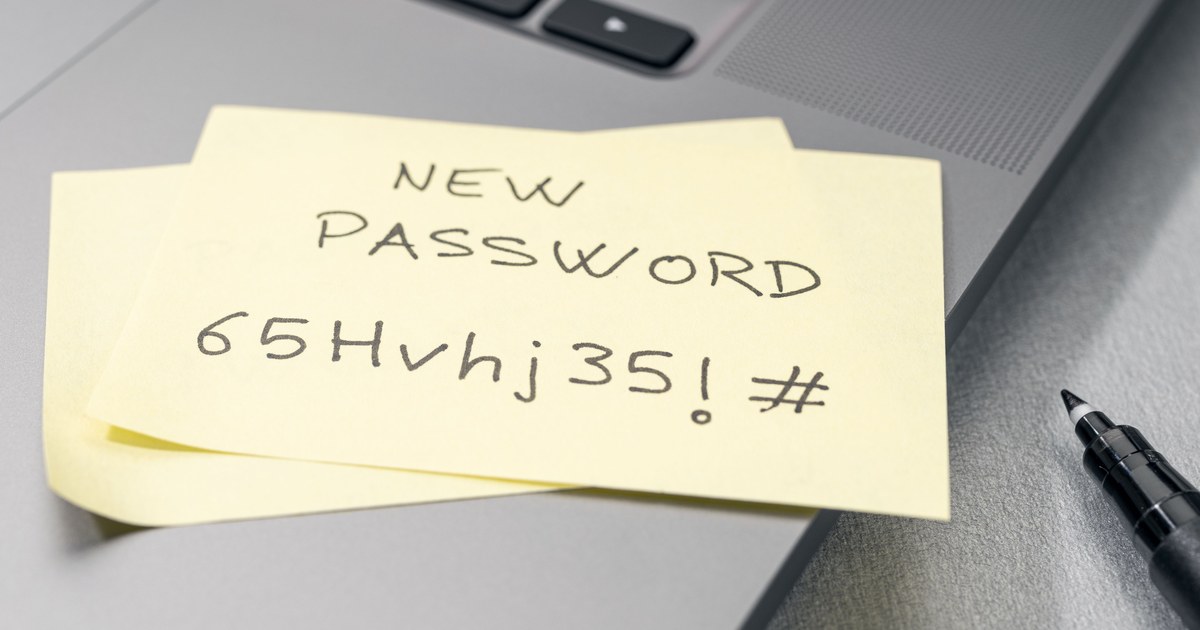
Her instinct was right. Like most charities we take on, their tech had grown the way these things do: a donated laptop here, a personal Gmail account there, a shared password on a sticky note because “we’re all volunteers, we trust each other”.
It got me thinking. There is a quiet assumption in the sector that compliance is a big business problem. Something for banks, law firms and corporates with IT departments. It isn’t. If you hold personal data, take donations or deliver services for a council, the rules apply to you too.
Charities are already targets
Roughly 57,000 UK charities reported a cyber breach or attack in the last year. That is 28% of the sector, according to the government’s Cyber Security Breaches Survey 2025/2026, published in April.
The rest of the numbers are what worry me:
- Only 38% of charities use multi-factor authentication, the single cheapest way to stop most account takeovers.
- Just 19% have a formal incident response plan.
- Only 9% have checked the security of their immediate suppliers.
- Cyber security is a high priority for senior leaders in 60% of charities, down from 68% the year before.
Phishing is still the main way in. It hit a quarter of all charities, and for most of those affected it was the only type of attack they saw. Criminals don’t need clever hacking when one convincing email to a volunteer will do.
The supplier point is not theoretical either. This summer a security incident at Beacon, a CRM widely used for donations and supporter records, led a number of charities to file serious incident reports with the Charity Commission. Those charities did nothing wrong themselves. Their data still sat on someone else’s system.
What “compliant” actually means for you
There is no special, lighter rulebook for charities. The same UK laws and expectations apply, and a few extra ones sit on top.
- UK GDPR and the Data Protection Act 2018. If you hold names, addresses, health details, safeguarding notes or Gift Aid records, you are a data controller. Most charities also pay the ICO’s lowest-tier data protection fee. There is a narrow not-for-profit exemption from the fee, but being exempt from the fee does not exempt you from the law.
- Trustee duties. The Charity Commission’s cyber crime guidance is clear that trustees must be aware of the risks, take reasonable steps to protect the charity, and respond properly if attacked. That is a governance duty, not an IT nice-to-have.
- Serious incident reporting. A breach that causes significant harm or loss may need reporting to the Charity Commission, and personal data breaches may need reporting to the ICO within 72 hours.
- Public sector contracts. Under PPN 014, central government requires Cyber Essentials for certain contracts, especially where personal data is handled. Councils and NHS bodies increasingly apply the same approach when they commission services from voluntary groups.
- Funders and partners. More grant makers and referral partners now ask how you protect data before they share it or fund you.
The same applies to parish councils, academies, community interest companies and small public bodies. If you handle public money or people’s personal information, you are expected to look after it properly.
What we usually find on day one
Every charity is different, but the same handful of gaps come up again and again when we onboard one:
- Personal accounts doing charity work. Volunteers using their own Gmail or Hotmail for beneficiary emails. When they leave, the data leaves with them.
- Shared logins. One “office@” password used by six people, with no idea who did what.
- No multi-factor authentication. Usually because nobody has switched it on, not because anyone decided against it.
- Old and donated kit. Laptops running out-of-support versions of Windows, with no encryption and no remote wipe if one goes missing.
- Files everywhere. Spreadsheets of names and addresses on USB sticks, home PCs and personal Dropbox accounts.
- Wide open Wi-Fi with no filtering. One network for staff, volunteers and visitors, with the password pinned to the wall. Anyone in the building sits on the same network as the laptop holding beneficiary records, and with no content filtering, nothing stops harmful sites being reached on your connection. If children or vulnerable adults use your space, that is a safeguarding issue too.
- No leaver process. Former trustees and volunteers who still have access years later.
- Backups nobody has tested. Or no backups at all.
None of this comes from carelessness. It comes from good people being stretched thin and tech growing organically. But every one of those gaps is a data protection risk, and most are cheap to fix.
Where to start, without blowing the budget
Most of the fixes cost little or nothing. Here is the order I would tackle them in.
- Take the free health check. The NCSC’s Small Charity Guide and its online “Check your cyber security” tool give you a plain-English starting point in minutes.
- Switch on multi-factor authentication. Email first, then anything holding money or personal data.
- Move everyone onto organisation accounts. Microsoft still offers eligible charities up to 300 free Business Basic licences, and Business Premium at up to 75% off. The old 10 free Business Premium seats ended at renewal from July 2025, so check what you are actually on.
- Get a joiners and leavers routine. When someone leaves, their access goes the same day.
- Update, encrypt and manage your devices. Including the donated ones.
- Back up properly, and test it. Microsoft 365 is not a backup on its own.
- Write a one-page incident plan. Who to call, who decides, and when to report to the ICO, the Charity Commission and Action Fraud.
- Ask your suppliers the awkward questions. Where is our data, who can see it, and what happens if you are breached?
- Aim for Cyber Essentials. It covers the basics, opens doors to public sector work, and smaller organisations certifying their whole organisation can get cyber insurance included.
- Put cyber on the trustee agenda. Name a trustee to own it, and review it at least once a year.
Good causes deserve good IT
The people who trust charities with their data are often the most vulnerable in our communities. They deserve the same protection a bank customer gets. Probably more.
You don’t need a big budget to get there. You need someone to look at what you have, fix the obvious gaps, and help your trustees understand where they stand.
Let’s have a conversation
At Westlake IT we have supported charities, community groups and public sector organisations across the South of England for over 21 years. If you would like a friendly, no-jargon review of where your organisation stands, get in touch. Call 023 9200 7850 or email info@westlake-it.co.uk. Consider IT done.